Global ISO Certification Consultant Services – Qualitcert

QualitCert Get a Quote

ISO Certifications

australia

Consulting &

ISO Certifications

-ISO Certification-

ISO 27001 Certification Services in Australia

QUALIT

CERT

CONSULTING AND ISO CERTIFICATIONS

Businesses can improve their information security management systems (ISMS) in accordance with international standards by using Qualitcert’s ISO 27001 certification services in Australia. The purpose of ISO 27001 is to preserve sensitive information, defend against online attacks, and guarantee adherence to data protection regulations. From preliminary risk assessments and gap analyses to implementation assistance and final certification audits, Qualitcert offers a holistic approach. Their services, which are customized for different industries, guarantee that businesses can successfully manage information security threats while proving to stakeholders and clients their dedication to data integrity and confidentiality. This certification improves market trust and company reputation in addition to fortifying security procedures.

Get In Touch

Test
Consultants Consultants
afd9a249 perf wp theme group 8796 Consultants Consultants
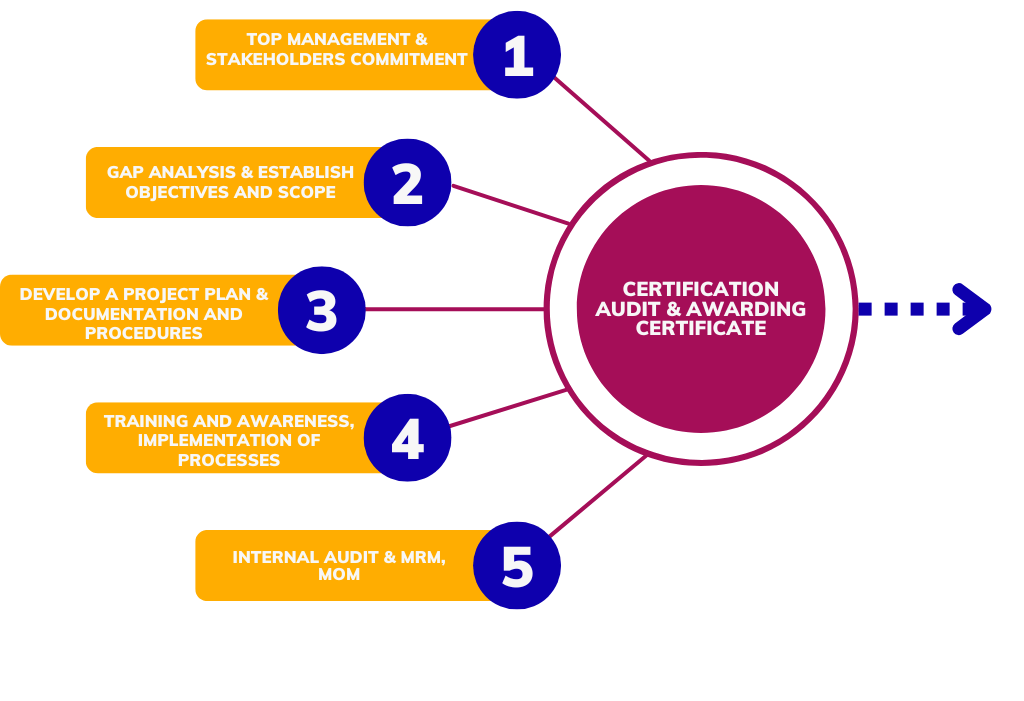
Approach and Methodology used to implement Management System Standard
Colorful Minimalist Linear Steps Circular Diagram 1 e1712599893569 Consultants Consultants

Implementing an ISO  standards involves a structured methodology to ensure that the organization effectively meets the requirements of the chosen standard and achieves certification. Sometimes defined methodology may vary depending on factors such as the size of the organization, its industry, and the complexity of the ISO standard being implemented, the following steps provide a basic framework

Ellipse 6 copy Consultants Consultants
OUR
Process

1, Determine the ISO Standard

2. Understand the Requirements

3. Training and Awareness

4. Implement the System

5. Internal Audit

6. Certification

partner_img Consultants Consultants
Benefits of having ISO Certification

Enhanced Credibility and Reputation

Legal and Regulatory Compliance

Enhanced Customer Satisfaction

Access to Global Markets

Environmental Sustainability

Information Security

Our Achievements and Success
Professional Experts
0 +
Years Experience
0 +
Projects
0 +
Satisfied Customers
0 %
Our Clients
WhatsApp Image 2023 05 12 at 8.24.31 PM e1684164170667
WhatsApp Image 2023 05 12 at 8.16.53 PM e1684163940587
WhatsApp Image 2023 05 12 at 8.22.55 PM
WhatsApp Image 2023 05 12 at 8.04.13 PM 3 e1684163886384
WhatsApp Image 2023-05-12 at 8.15.32 PM
OUR
SERVICES
ISO 9001 Certification
ISO 45001 Certification
ISO 14001 Certification
ISO 22000 Certification
ISO 13485 Certification
ISO 27001 Certification
ISO 20000-1 Certification
ISO 29001 Certification
ISO/IEC 27001 for Australia Organisations

ISO/IEC 27001 Consulting and Readiness Services in Australia

Build a practical Information Security Management System that helps Australia organisations manage information-security risk through a defined ISMS scope, treatment plan, Statement of Applicability and Annex A controls with clear ownership, current evidence and assessment readiness.

Connect Information Risk Decisions to an Operable ISMS

Australia's financial, cloud, healthcare, government-facing and professional-service organisations process sensitive information across systems and suppliers. Australia's financial, government-facing, cloud, healthcare and professional-service organisations process sensitive information across systems and suppliers. Australia's financial, government-facing, cloud, healthcare and professional-service organisations process sensitive information across systems and suppliers. Australia's logistics, healthcare, financial, cloud and professional-service organisations process sensitive information across systems and suppliers. Australia's banking, cloud, government-facing, healthcare and professional-service organisations process sensitive information across systems and suppliers. Australia's banking, cloud, government-facing, healthcare and professional-service organisations process sensitive information across systems and suppliers. Australia's banking, cloud, government-facing, healthcare and professional-service organisations process sensitive information across systems and suppliers. Australia's industrial, logistics, healthcare, fintech and professional-service organisations process sensitive information across sites, cloud platforms and suppliers. Australia's banking, fintech, cloud, professional-service and healthcare organisations process sensitive information across customers, suppliers and regional operations. Australia's cloud, fintech, free-zone, hospitality and professional-service organisations process sensitive information across international customers and suppliers. Successful ISO/IEC 27001 work begins with scope. The organisation must be clear about which activities, sites, products, systems and third parties belong within the Information Security Management System.

Once scope is established, Qualitcert evaluates the risks and obligations associated with ISMS scope, risk assessment and treatment and Statement of Applicability.

Procedures and evidence are then developed around Annex A controls and supplier security, with practical checks to confirm that stated controls match actual behaviour.

The final stage reviews incident and resilience evidence, open actions and management oversight so the organisation can approach the certification audit with a coherent evidence trail.

Australia Operating Context

Information Security Across Australia's Cloud, Product and Service Economy

Australia organisations use ISO/IEC 27001 to improve assurance where ISMS scope, risk assessment and treatment and Statement of Applicability cross teams, suppliers or technical systems.

Cloud platforms, financial systems, customer data, critical suppliers and remote work create an information-security environment that requires risk-based governance.

Common readiness problems arise when ISMS scope is treated separately from risk assessment and treatment and Statement of Applicability, creating duplicated controls or incomplete evidence.

Qualitcert structures the work so Annex A controls, supplier security and incident and resilience evidence can be reviewed together by operational leaders and specialist teams.

Operational and Assurance Value

Operational Benefits of ISO/IEC 27001 in Australia

The value comes from making ISMS scope, risk assessment and treatment and Statement of Applicability easier to manage, measure and explain.

Clearer Isms Scope

Defines ownership, criteria and evidence for ISMS scope across the agreed scope.

Stronger Risk Assessment And Treatment

Connects risk assessment and treatment to practical controls rather than isolated policy statements.

More Reliable Statement Of Applicability

Makes Statement of Applicability easier to monitor, test and improve with current records.

Better Annex A Controls

Supports consistent decisions about Annex A controls during normal work and change.

Industry Applications

Where ISO/IEC 27001 Applies in Australia

The examples below show how the Information Security Management System changes with the operating model, risk profile and evidence needs of each sector.

01

Financial, Cloud and Critical-Service Providers

Govern identities, cloud workloads, customer data, supplier access and incident response.

02

BPO and Shared Services

Protect client information across teams, shifts, endpoints and subcontractors.

03

Fintech Platforms

Control privileged access, transaction systems, interfaces and monitoring.

04

Health Technology

Protect patient, diagnostic and operational data across connected systems.

05

Engineering and R&D Centres

Secure design files, source code, prototypes and collaboration environments.

06

Data Centres and Managed Services

Coordinate physical, logical, operational and continuity controls.

Implementation Route

How ISO/IEC 27001 Readiness Is Built

The sequence moves from scope and current-state review to operating evidence and preparation for the certification audit.

01

Define Isms Scope

Confirm boundaries, responsibilities and criteria for ISMS scope.

02

Assess Risk Assessment And Treatment

Review current practices, risks and evidence relating to risk assessment and treatment.

03

Design Statement Of Applicability

Create proportionate controls and records for Statement of Applicability.

04

Implement Annex A Controls

Assign owners, train relevant personnel and operate Annex A controls.

05

Verify Supplier Security

Test the effectiveness and consistency of supplier security.

06

Improve Incident And Resilience Evidence

Close gaps and strengthen incident and resilience evidence before the certification audit.

Records and Control Evidence

Evidence Commonly Prepared for ISO/IEC 27001

The final evidence set depends on scope, risk, customer obligations and the selected certification audit route.

Typical ISO/IEC 27001 Records

  • Scope, applicability and responsibility statement
  • Isms Scope register or criteria
  • Risk Assessment And Treatment assessment records
  • Statement Of Applicability procedure or control matrix
  • Annex A Controls operating evidence
  • Supplier Security monitoring or test results
  • Incident And Resilience Evidence review records
  • Competence, awareness and communication evidence
  • Internal review, findings and corrective-action log
  • Management approval and certification audit readiness record
Records should be current, approved, traceable and maintained by the people who operate the controls.

Weak Points to Correct Early

These issues commonly weaken ISO/IEC 27001 readiness or create avoidable questions during the certification audit.

  • Defining ISMS scope without linking it to the real operating scope.
  • Assigning no accountable owner for risk assessment and treatment.
  • Documenting Statement of Applicability without current operating evidence.
  • Leaving changes that affect Annex A controls outside formal review.
  • Approaching the certification audit before supplier security and incident and resilience evidence have been tested.
Early correction reduces document rework and gives process owners time to produce credible evidence.
Contextual Australia Resources

Review ISO/IEC 27001 services in Australia for the exact Australia service resource available in the uploaded workbook.

Review PCI DSS services in Australia where shared governance, evidence, risk or operational controls can be aligned.

Review a direct discussion about ISO/IEC 27001 implementation in Australia to confirm scope, evidence needs and the appropriate assessment route.

Frequently Asked Questions

ISO/IEC 27001 Questions from Australia Organisations

These answers focus on scope, implementation evidence and preparation for the certification audit.

What business problem does ISO/IEC 27001 address for Australia organisations?

It provides a structured way to manage information-security risk through a defined ISMS scope, treatment plan, Statement of Applicability and Annex A controls while creating clear ownership and reviewable evidence.

Which Australia operations usually consider ISO/IEC 27001?

It is commonly relevant to Software and SaaS Providers, BPO and Shared Services, Fintech Platforms and other organisations with comparable assurance needs.

How should the scope for ISO/IEC 27001 be determined?

Scope should reflect the actual sites, services, products, systems, people and third parties needed for the Information Security Management System to achieve its intended outcome.

Why is ISMS scope important in ISO/IEC 27001 readiness?

Isms scope establishes the boundaries and decision criteria needed to make later controls and evidence coherent.

What evidence supports risk assessment and treatment under ISO/IEC 27001?

Evidence normally includes approved criteria, assigned responsibilities, operating records, monitoring results and actions taken when requirements are not met.

How is Statement of Applicability checked before the certification audit?

Qualitcert reviews design, implementation and sampled evidence to confirm that Statement of Applicability is applied consistently across the agreed scope.

Can ISO/IEC 27001 be coordinated with ISO/IEC 27701?

Yes. Shared governance, risk, competence, document control, audit and improvement activities can often be aligned without losing service-specific requirements.

What common gap delays ISO/IEC 27001 readiness?

A frequent gap is having policies without current evidence that owners understand and operate the controls related to Annex A controls.

What should management review before the certification audit for ISO/IEC 27001?

Management should review scope, performance, open risks, findings, resources, changes and whether supplier security and incident and resilience evidence are effective.

How does Qualitcert support ISO/IEC 27001 implementation in Australia?

Qualitcert provides gap review, implementation planning, document and control development, training, internal review and readiness support without acting as the independent assessor.

Discuss ISO/IEC 27001 Readiness

Build a Practical ISO/IEC 27001 Programme in Australia

Share your scope, current controls and target certification audit. Qualitcert can review gaps and define a proportionate implementation plan.

Plan ISO/IEC 27001 Readiness →
Scroll to Top